让 Agent 的身份、工作与责任链进入统一控制面Bring Agent Identity, Work, and Accountability Into One Control Plane
川序不是新的 Agent 框架,而是框架中立、Skill-first 的管理基础设施。Agent 可以由平台内外不同运行时承载,但必须注册、认证并经过受控边界后才进入治理范围。Chuanxu is not another Agent framework. It is framework-neutral, Skill-first management infrastructure. Agents may run inside or outside the platform, but only registered, authenticated traffic through controlled boundaries is governed.
v5.0.4
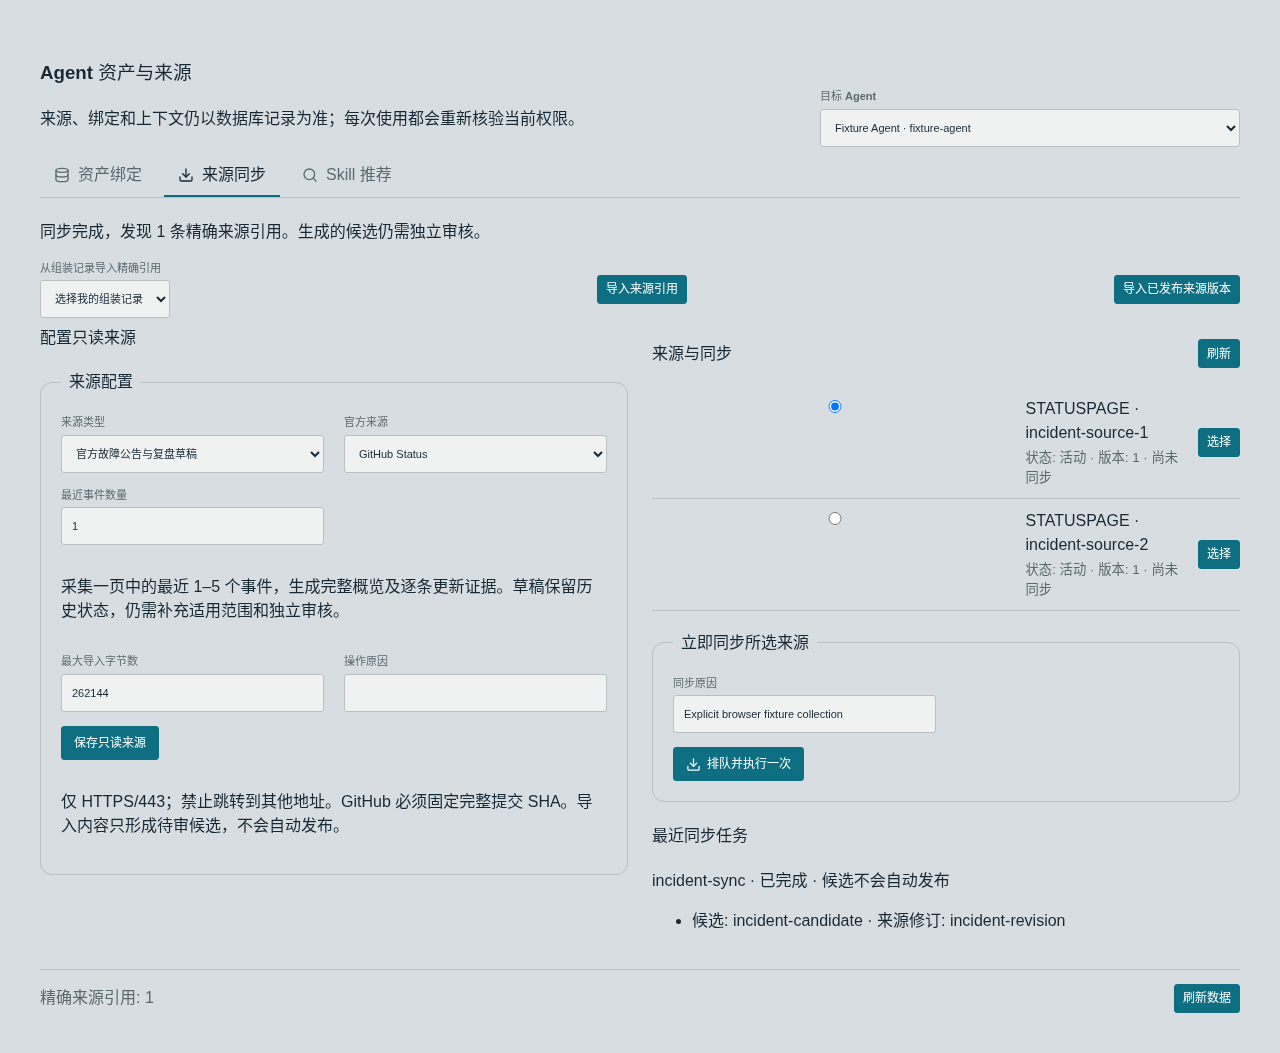
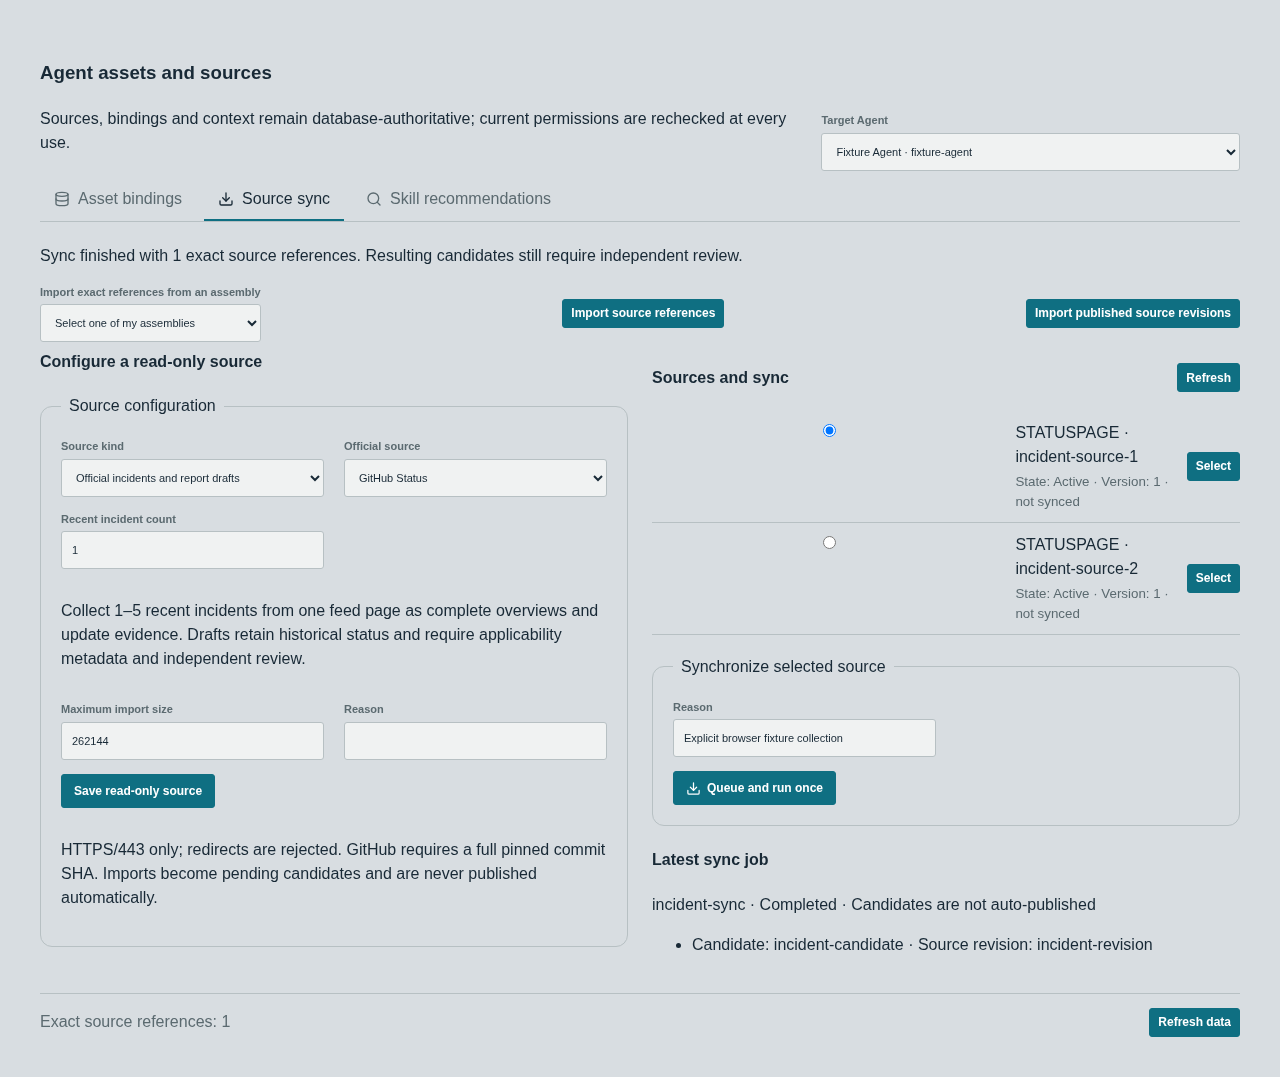
官方事件来源接入Official incident sources
从 GitHub、Cloudflare 官方状态接口有界采集,保留原始快照、事件时间、精确修订与幂等记录;沿用 Source、Task 和候选审核,采集不自动发布。Collect bounded GitHub and Cloudflare status records with raw snapshots, event times, exact revisions and idempotency. Reuse Source, Task and candidate review; collection does not publish knowledge.
v5.0.4
带证据的故障复盘草稿Evidence-linked incident report drafts
参考 PagerDuty 开放模板整理事实、时间线、证据与缺口。根因和企业内部影响未知时明确保留,建议待确认;独立审核与显式晋升后才能复用。Use an attributed PagerDuty-based structure for facts, timelines, evidence and gaps. Unknown root causes and internal impact remain unknown; advice needs confirmation, independent review and explicit promotion.
v5.0.4
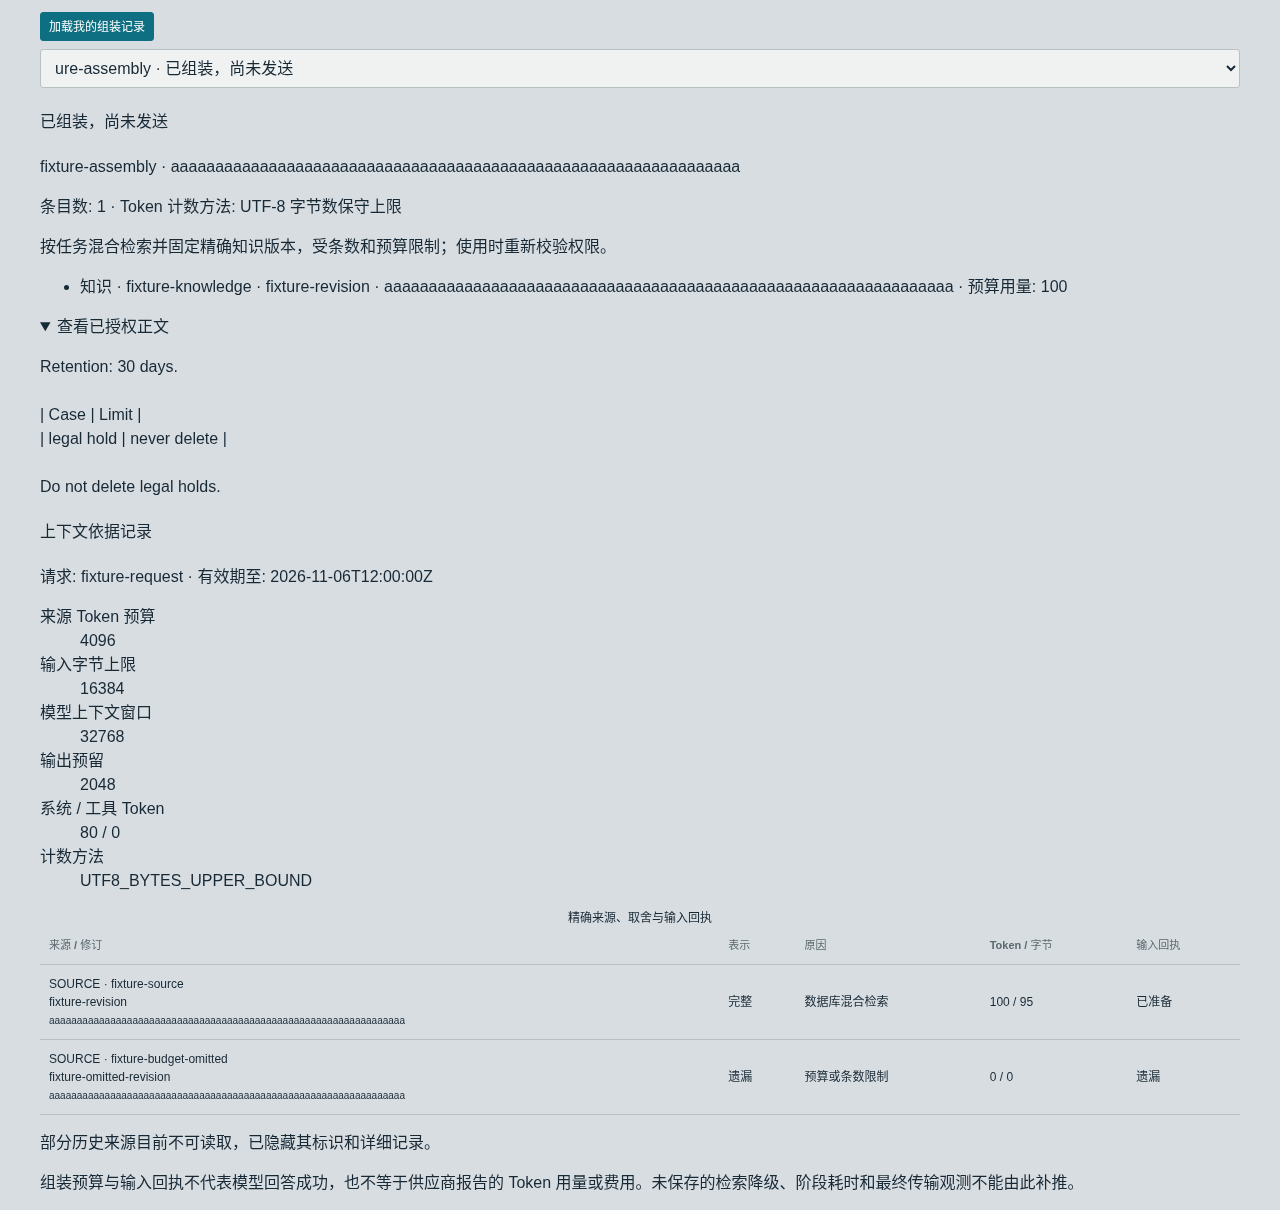
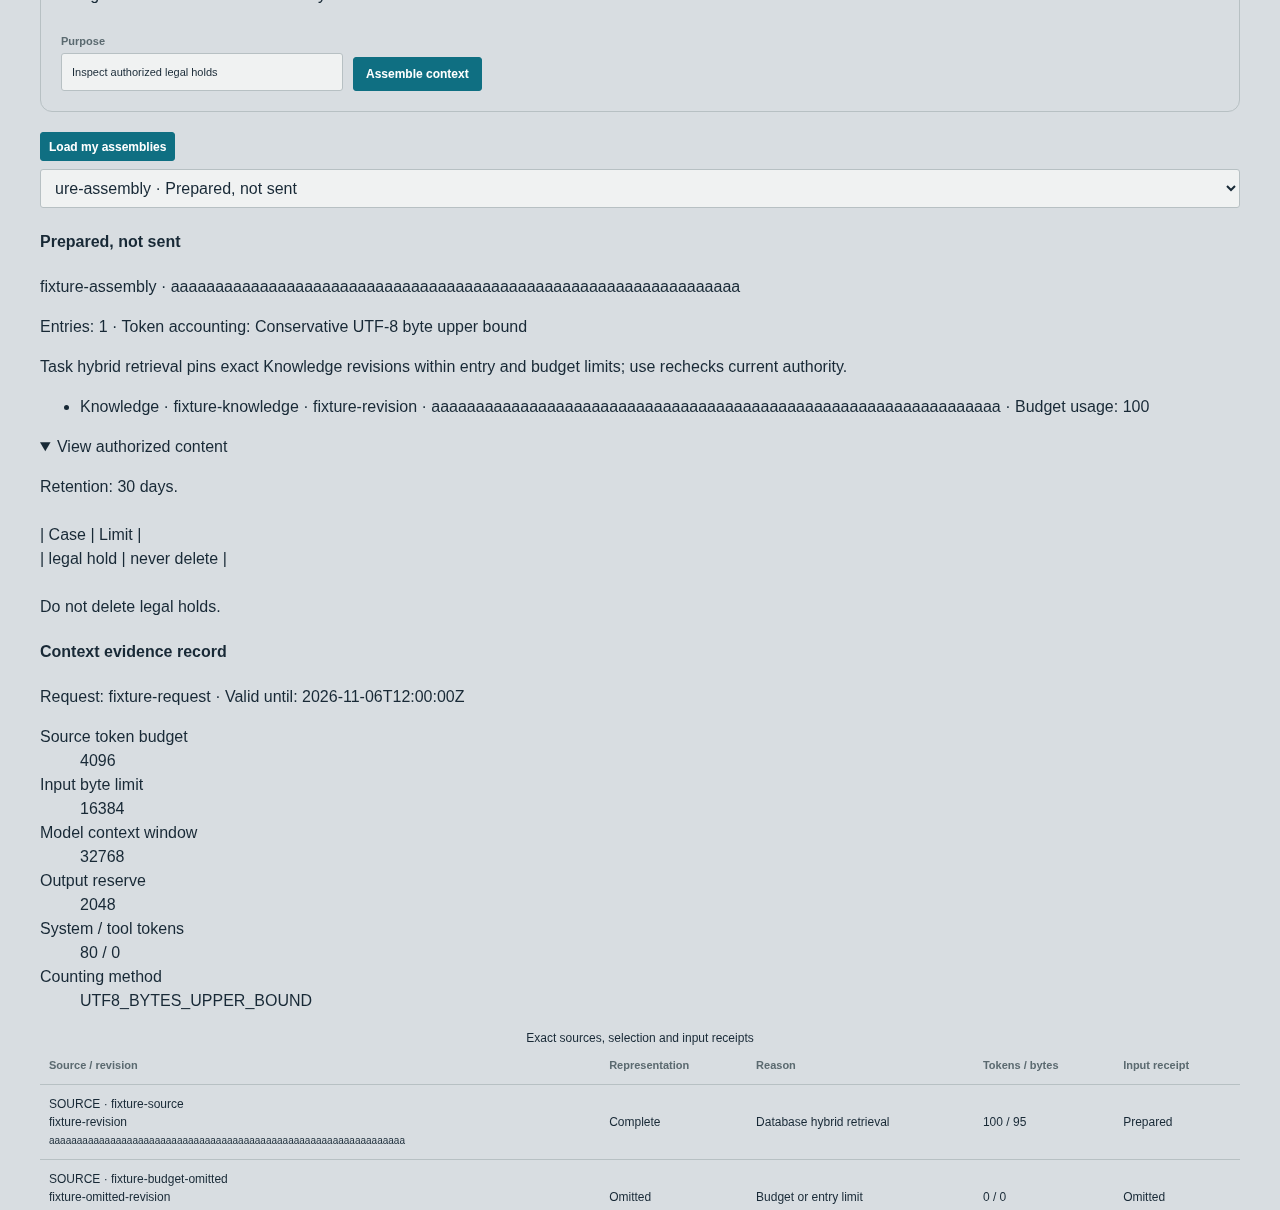
上下文装配依据Context assembly evidence
沿用预算、表示和来源修订记录,查看选用、遗漏与降级原因;准备完成不等于已发送,使用时继续核对来源、有效期和当前授权。Reuse budgets, representations and source revisions to explain selection, omissions and fallback. Preparation is distinct from dispatch; use rechecks sources, expiry and current grants.
v5.0.4
同轮准备成本测量Same-turn preparation measurements
已测量显式来源与混合检索的准备路径,保留当前授权重验。不增加 query/TTL 缓存,不以局部耗时观测承诺 Token、费用或普遍性能收益。Measure explicit-source and mixed-retrieval preparation while retaining current authorization checks. No query/TTL cache is enabled; local timings establish no Token, cost or general performance guarantee.
v5.0.4
最终输入与完整输出检查Final input and complete output checks
公共 native transport 检查完整 Provider JSON 文本,并发送同份序列化字节。完整输出继续校验;托管图片像素语义与独立 DispatchTicket 字节审计仍有边界。The common native transport checks final Provider JSON text and sends the same serialized bytes, with complete output validation. Hosted-image pixel semantics and independent DispatchTicket byte auditing retain explicit limits.
v5.0.4
共享编码研究保持关闭Shared encoding research remains disabled
共享编码仅完成实验设计,默认关闭。模型摘要仍需逐项核对来源,结构有效不能代替事实、根因或业务验收;不宣称全面 DLP。Shared encoding has an experiment design and remains disabled. Generated summaries need source review; structural validity establishes neither facts, root causes nor business acceptance. No comprehensive DLP claim is made.
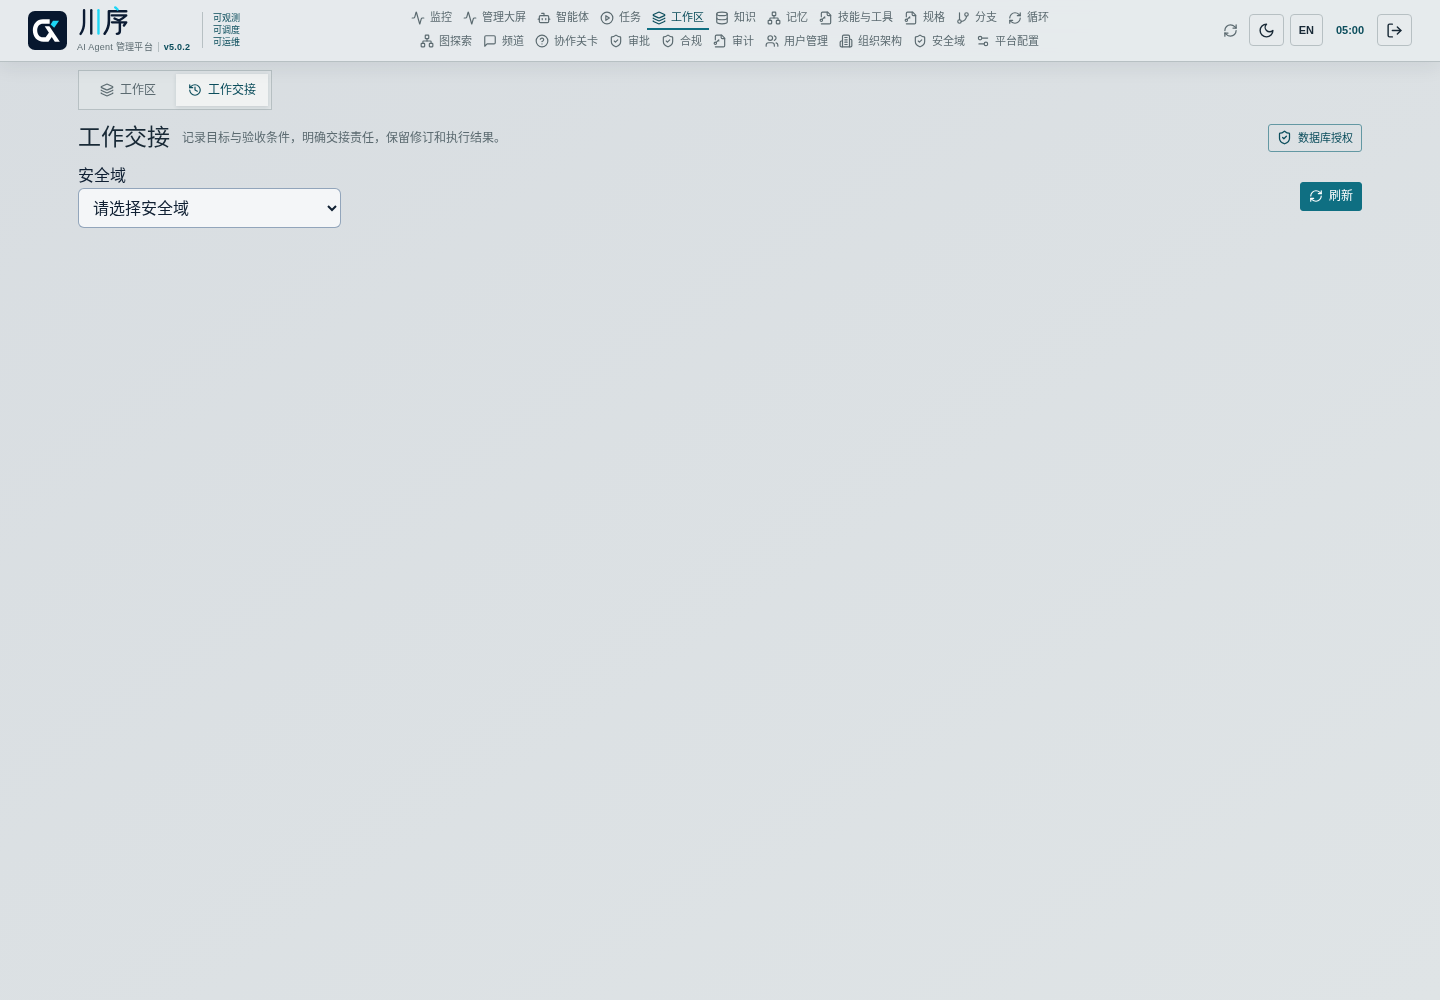
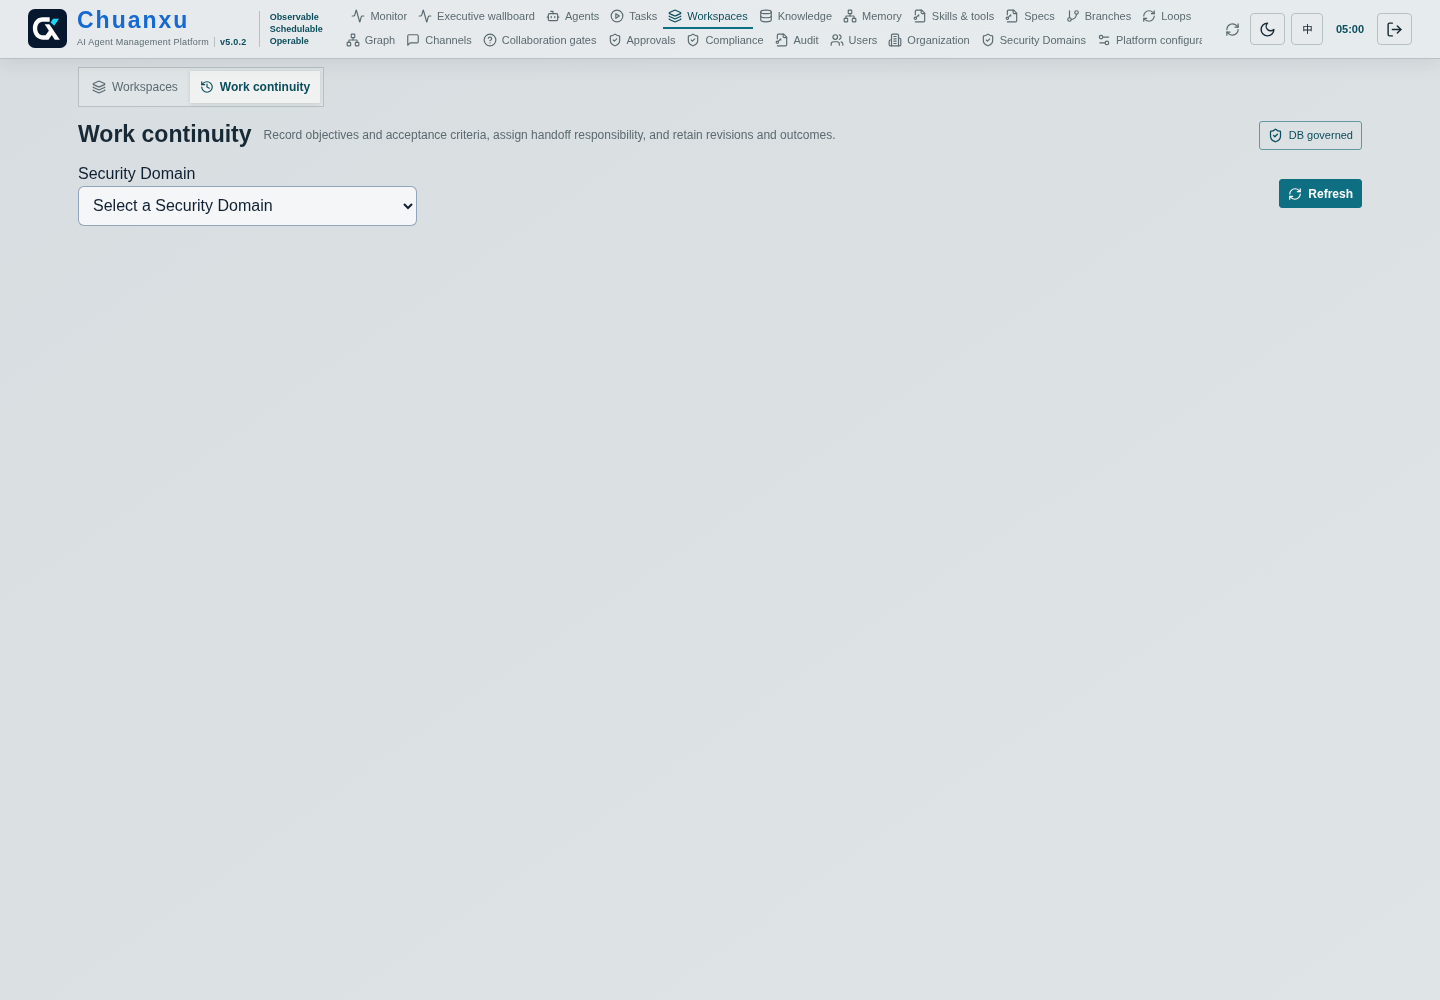
当前界面示例Current interface examples
事件来源 · 测试数据示例 / Incident sources · test data事件来源 · 测试数据示例 / Incident sources · test data上下文依据 · 测试数据示例 / Context evidence · test data上下文依据 · 测试数据示例 / Context evidence · test data
川序社区版与企业版共享基于数据库的身份、任务、协作关卡、属性图、DB4A2A、知识和记忆能力,按部署和治理需求选择交付方式。Chuanxu Community and Enterprise share database-backed Identity, Tasks, collaboration gates, property graphs, DB4A2A, Knowledge and Memory. Choose a delivery that fits your deployment and governance needs.
川序 Chuanxu Community
一个整合包,部署时选择 Oracle、PostgreSQL 或 YashanDB,Apache-2.0。One unified Apache-2.0 package; select Oracle, PostgreSQL or YashanDB at deployment.
川序 Chuanxu Enterprise
Oracle、PostgreSQL、YashanDB 三个独立企业包,BSL-1.1,按商业许可交付。Three separate Oracle, PostgreSQL and YashanDB Enterprise packages under BSL-1.1 and commercial delivery terms.
每个进程固定使用一个底座;切换需重启和独立数据库准备,不会自动迁移数据。产品名不同不代表升级包可以互换。Each process uses one backend. Switching requires restart and a separately prepared database; it does not move data. Different product identities do not make upgrade packages interchangeable.
持续工作与交接Work Continuity
换一个接收者,工作仍有明确目标与依据Keep Objectives and Evidence Clear Across Handoffs
工作契约记录目标、责任与验收条件;交接明确接收者和约定版本,并保留修订、确认与结果。继续执行时,将有权使用的任务、知识和历史按确切版本组装为上下文,记录选择原因和实际输入;源对象或双方权限变化后重新校验。Work contracts record objectives, responsibility and acceptance criteria. Handoffs identify recipients and agreed revisions, retaining changes, acknowledgements and outcomes. Subsequent execution assembles authorized tasks, knowledge and history at exact revisions, records selection reasons and actual inputs, and rechecks source objects and both parties' current permissions.
成果先作为候选进入独立审核,再明确沉淀为记忆、知识、经验或 Skill。签名 Skill 可由受管 Linux 客户端在协作式安全点切换,保留旧版本;这不代表能隔离或独立观测所有外部进程。诊断分别展示失败、不可用和未观测,不将没有执行的检查标记为通过。Results enter independent candidate review before explicit promotion to memory, knowledge, experience or Skills. A managed Linux client can switch signed Skills at cooperative safe points while retaining earlier versions; this does not isolate or independently observe arbitrary external processes. Diagnostics distinguish failure, unavailability and unobserved state, without passing checks that never ran.
v4.5.1 按需扩展v4.5.1 Governed Extensions
接入更多能力,仍保留明确的权限与执行依据Extend Capabilities With Clear Authority and Evidence
模型先实测能力,工具与技能先发现再加载确切版本;上下文保留来源、约束和未完成工作。Portal 与频道共用回答质量流程,进度、取消和只读诊断帮助使用者判断正在发生什么。Probe model support before use, discover Tools/Skills before loading exact versions, and preserve context sources, constraints and incomplete work. Portal and Channels share answer-quality flows, while progress, cancellation and read-only diagnostics explain execution state.
可控的外部接入Governed Integrations
登记的 MCP 只读工具、有限 A2A 任务、仅元数据遥测和固定隔离框架各自授权。Registered read-only MCP Tools, bounded A2A tasks, metadata-only telemetry and one pinned isolated framework are authorized independently.
持续工作有依据Traceable Continuing Work
预算与派生内容重新核对原始来源;草稿、分叉、离线回放与预检保留确切版本。Budgets and derivations recheck original sources; drafts, forks, offline replay and preflight preserve exact versions.
图片与文档输入Managed Image and Document Input
受管上传核对格式、大小、权限和模型支持;内容作为资料,不产生工具授权。Managed uploads check format, size, authorization and model support; their contents are data, not Tool authority.
v4.5.2 统一任务连续性v4.5.2 Unified Task Continuity
让 A2A 与 DB4A2A 复用同一套数据库事实Reuse One Database Fact Chain for A2A and DB4A2A
标准 A2A、DB4A2A 与多步骤 MCP 工作统一关联稳定任务 ID、任务计划、步骤、租约、围栏令牌、尝试、Outbox、上下文版本和审计记录。现有协作关卡、分支和实体图继续作为数据库投影复用;图边、协议消息和模型输出都不会授予权限。Standard A2A, DB4A2A, and multi-step MCP work share stable task IDs, Task Plans, Steps, leases, fencing tokens, attempts, Outbox, context revisions, and audit records. Existing collaboration gates, branches, and entity graphs remain database-backed projections; graph edges, protocol messages, and model output never grant authority.
幂等与围栏Idempotency and Fencing
重复 admission 复用同一任务;租约过期或围栏不匹配时拒绝陈旧写入。Repeated admission reuses one task; expired leases and stale fencing tokens reject old writes.
未知结果可恢复Recover Unknown Sends
外部发送未确认时记录 UNOBSERVED,按持久业务键协调,不盲目重发副作用。Unconfirmed external sends remain UNOBSERVED and reconcile by durable business key instead of blindly repeating effects.
让交接结论保留版本、来源和适用边界Keep versions, sources and applicability with handoff findings
记忆记录事件、观察和适用时间,版本协调需独立审核,历史恢复生成新的后继版本。工作便签绑定确切工作和来源版本,可记录发现、未决问题和下一步;便签到期或退役后保留历史,不自动发布为长期记忆。Memory records event, observation and applicability times. Reconciliation requires independent review; history restoration creates a new successor version. Working notes bind exact Work and source revisions for findings, open questions and next actions. Expired or retired notes retain history and never publish themselves as long-term Memory.
v5.0.1 · Agent 资产与上下文v5.0.1 · Agent assets and context
先选择确切依据,再按预算组装上下文Select exact evidence before assembling a bounded context
为 Agent 绑定获授权的记忆、知识、Skill 和来源版本,结合查询、用途与优先级选择元数据和内容。模型输入预算保留必需指令与约束,分别记录内容表示与实际交付事实;资产绑定不新增来源权限,每次使用仍复核授权。Bind authorized Memory, Knowledge, Skills and source revisions to an Agent. Select metadata and content using the query, purpose and priority. Model-input budgets retain required instructions and constraints, with separate records for content representation and actual delivery. Asset bindings grant no additional source permissions; authorization is rechecked at use time.
v5.0.1 · 回答质量验收v5.0.1 · Answer quality evaluation
把最终回答、引用和独立评审分开记录Record final answers, citations and independent review separately
验收用例和评分标准保留版本,最终回答绑定确切来源、策略与模型修订,加密保存输入与输出。事实正确性和引用质量分别由独立评审记录,检索准备与最终回答分开核对;模型发送结果不确定时记为未观测,不自动重发。Cases and rubrics retain versions. Final answers bind exact source, policy and model revisions, with encrypted input and output. Independent reviews record factual correctness and citation quality separately, distinguishing retrieval preparation from final answers. Uncertain model sends remain unobserved and are never resent automatically.
v5.0.1 · 知识回答与证据v5.0.1 · Grounded answers and evidence
回答依据、缺口和补充来源都可核对Review evidence, gaps and supplementary sources
Portal 与频道共享获授权的关键词、全文、向量和混合检索,记录实际使用的策略与降级情况。部分命中、主体歧义和资料矛盾分别呈现;通用模型补充与混合来源明确标注。排队回答在发送和发布前重新核对来源、模型配置与补充策略,频道还复核当前读者范围。Portal and Channels share authorized keyword, full-text, vector and hybrid retrieval, recording actual strategies and fallback behavior. Partial coverage, ambiguous subjects and conflicting sources remain distinct. General-model supplements and mixed-source answers are labeled. Queued answers recheck sources, model configuration and supplement policy before dispatch and publication; Channels also recheck current readers.
把指定文档带入可审核的知识流程Bring selected documents into a reviewable knowledge workflow
同步已配置的 HTTPS 文档,以及固定提交的 GitHub 目录或文件。任务与步骤保留进度,租约、围栏、幂等导入和原子检查点支持中断后的受控继续。同步记录保留来源版本,导入成果先进入待审核状态,经独立审核后才能发布;不自动抓取任意网站或持续信任已撤销的权限。Synchronize configured HTTPS documents and GitHub directories or files pinned to a commit. Tasks and steps retain progress; leases, fencing, idempotent imports and atomic checkpoints support controlled continuation. Records retain source revisions. Imports remain pending independent review before publication; synchronization does not crawl arbitrary sites or preserve revoked access.
v5.0.1 · 受控复盘与复用v5.0.1 · Governed retrospectives and reuse
让工作经验经过审核再沉淀Review work experience before making it reusable
工作便签记录发现、未决问题和下一步,交接引用确切版本。显式关联任务的复盘生成待审核候选,复用既有成果审核与发布流程;记忆协调另行记录独立评审。恢复历史时创建新的后继版本,保留原版本与审计,不倒退覆盖既有记录。Working notes record findings, open questions and next actions; handoffs reference exact versions. Explicit task-linked retrospectives create pending candidates for the existing review and publication workflow. Memory reconciliation records independent review. Restoring history creates a new successor version, retaining original versions and audit records instead of overwriting them.
v5.0.3 · 2026-11-03
按问题组合数据库检索Query-aware database retrieval
结合关系属性、全文、向量、标签与授权图关系选择资料;排序不增加模型生成调用,返回内容仍复核使用者和 Agent 的当前权限。Combine relational, full-text, vector, tag and authorized graph signals. Ranking adds no generation call; returned sources retain current user and Agent authorization.
v5.0.3 · 2026-11-03
保留可追溯的原始依据Traceable original evidence
正文关联来源、章节位置和精确版本;表格、代码、例外与限制可随来源保留。派生知识在使用时继续复核原始来源。Link content to its original location and exact revision. Retain tables, code, exceptions and conditions; derived knowledge rechecks original sources at use time.
v5.0.3 · 2026-11-03
引导知识入库Guided knowledge intake
填写用途、责任人、适用产品与版本、时间、密级和共享范围,预览分块并检查缺项、重复和冲突;上传成功不等于正式发布。Declare purpose, owner, applicability, time, classification and audience. Preview chunks and inspect missing details, duplicates and conflicts before publication.
v5.0.3 · 2026-11-03
候选审核后发布Review candidates before publication
资料导入、来源同步与成果整理复用候选、独立审核和版本发布;保留原访问范围及历史,草稿不会自动成为共享回答依据。Imports, source synchronization and work outcomes reuse candidates, independent review and versioned publication. Preserve access scope and history; drafts never publish themselves.
v5.0.3 · 2026-11-03
按适用范围组织判断Applicability-aware evidence
检索与上下文保留版本、时间、缺失和冲突。事实、建议及成立条件应有依据;资料不足时明确缺口与需要人确认的事项。Preserve versions, time, gaps and conflicts in retrieval and context. Ground facts and conditional advice in sources, and identify missing evidence and decisions requiring a person.
v5.0.3 · 2026-11-03
按角色和目标学习Learning by role and goal
从学习目录查找当前产品的入门、权限、任务与排错指南,按需读取确切版本;安装资料和客户自有知识分别保留归属及权限。Find current-product onboarding, access, task and recovery guidance by role and goal. Load exact revisions on demand; product manuals and customer knowledge retain separate ownership and grants.
v5.0.3 · 2026-11-03
Agent 按需发现能力On-demand Agent capability discovery
先读取授权目录元数据,再加载所需指南或 Skill 的精确内容;能力说明不授予执行权限,操作前仍核对当前状态和接口合同。Discover authorized metadata before loading exact guidance or Skill content. Descriptions grant no execution rights; operations still check current capability state and interface contracts.
v5.0.3 · 2026-11-03
知识衔接持续任务Knowledge for continuing work
Task、Loop、Graph 与 DB4A2A 复用目标、批准决策、确切上下文和结果回执。步骤时间没有历史依据时保持未知,模型描述不代替真实完成。Tasks, Loops, Graphs and DB4A2A retain goals, approved decisions, exact context and outcome receipts. Unknown historical step times stay unknown; model text does not establish completion.
v5.0.2 · 1/8
可信的模型结果Reliable model results
区分完成、拒答、截断、格式错误与未知发送结果,避免把不完整输出当成成功。Distinguish completed, refused, truncated, malformed and unknown outcomes before accepting a result.
v5.0.2 · 2/8
共享模型容量与取消Shared model capacity and cancellation
端点别名共享明确的协调者与有界队列;取消区分排队、已发送和未确认状态,未知请求先协调再继续。Endpoint aliases share an explicit coordinator and bounded queue. Cancellation distinguishes queued, sent and unconfirmed work; unknown requests reconcile before continuing.
v5.0.2 · 3/8
可核对的模型观测Traceable model observations
记录排队、首字与总耗时,以及可获得的输入、输出、缓存和推理用量;缺失保持未知,不填成零,也不披露隐藏推理。Record queue, first-token and total timing with available input, output, cache and reasoning usage. Missing values stay unknown; hidden reasoning is never exposed.
v5.0.2 · 4/8
结构化候选与受控工具回合Structured candidates and governed tool turns
结构化复盘进入待审核候选;有界只读工具回合复用现有授权、独立审批与 Worker 围栏,模型输出不能自我授权或发布。Structured retrospectives become pending candidates. Bounded read-only tool turns retain authorization, independent approval and Worker fencing; model output cannot authorize or publish itself.
v5.0.2 · 5/8
上下文与数据库批处理Context and database batching
批量读取来源、权限与内容表示,并在事务中批量写入;相同内容减少重复输入,同时保留来源标识、义务与当前授权,工具和 Skill 按预算加载。Batch source, permission and representation reads and transactional writes. Deduplicate equal input bodies while retaining identities, obligations and current authorization; load Tools and Skills within budget.
v5.0.2 · 6/8
处理诊断与受控恢复Processing diagnosis and governed recovery
沿原 Task、尝试、Loop 与 Graph 诊断阻塞、无进展和重复工具调用,恢复保留原预算;已完成工作不重跑,未知副作用不盲目重发。Diagnose blocking, no progress and repeated tools along the original Task, attempt, Loop and Graph. Recovery preserves budgets, skips completed work and reconciles unknown effects before any resend.
分别适配 MCP 2026-07-28 的已声明发现与只读子集,以及 2025-06-18、2025-11-25;重新发现复核身份、版本与审批,不宣称完整 MCP Tasks 支持。Separate adapters cover the declared discovery/read-only subset of MCP 2026-07-28 and both 2025 revisions. Rediscovery rechecks identity, version and approval; full MCP Tasks support is outside this scope.
v5.0.2 · 8/8
结果、过程与效率验收Result, process and efficiency evaluation
回答、引用、过程与效率绑定确切包和用例;已观测回答导入后不重新生成,由独立 Human 逐条审核并导出不可变记录,脚本不得代审,否决阻断发布。三库新装与声明升级分别验证。Bind answers, citations, process and efficiency to exact packages and cases. Import observed outputs without regeneration; an independent Human reviews each output and exports immutable records. Scripts must not decide; a negative review blocks release. Verify each database, fresh install and declared upgrade separately.
已观测回答的独立 Human 审核Independent Human review of observed answers
109 号迁移支持登记、读取、逐条审核和导出已完成回答的原始观测。Dashboard 各次操作使用真实 Human 会话,复核当前平台管理、安全域、Agent、确切 Profile 修订和已披露来源权限;写入另需 CSRF。导入不会请求模型,也不会成为新的原生回答质量生成任务。Migration 109 supports registering, reading, reviewing and exporting original observations of completed answers. Every Dashboard operation requires a real Human Session and rechecks current platform-management, Domain, Agent, exact Profile revision and disclosed-source authority; writes also require CSRF. Import neither calls a model nor creates a native answer-quality generation run.
审核人须同时区别于登记人和原责任人,针对完整原始观测(含输出)的确切摘要逐条判断事实正确性与引用支持,并填写理由。真实 Human 决定须由本人提交,脚本或模型不得代审;登记记录不能充当审核结论。The reviewer must differ from both the registering actor and the original responsible actor, decide factual correctness and citation support for each exact complete observation digest, and give a reason. The Human must submit the actual decision personally; scripts and models must not act as reviewers. Registration is not a verdict.
原始不可变集合、输出、审核和必要审计可在授权下导出,记录与审计同事务提交。发布仍独立核验原始捕获来源、确切包和完整用例覆盖;缺失、失效或否定的审核阻断验收。导入、人工审核和最终发布验收分别留证,最终日期仍来自完成打包。Authorized export retains original immutable sets, outputs, reviews and required audit; records and audit commit together. Release independently checks original capture provenance, exact packages and complete case coverage; missing, stale or negative reviews block acceptance. Import, Human review and release acceptance need separate evidence; the final date still follows completed packaging.
v5.0.1 可选模型网关v5.0.1 Optional Model Gateway
在不强制改造全部 Agent 的前提下,建立 Token、配额与成本事实Build Token, Quota, and Cost Evidence Without Forcing Every Agent Through One Route
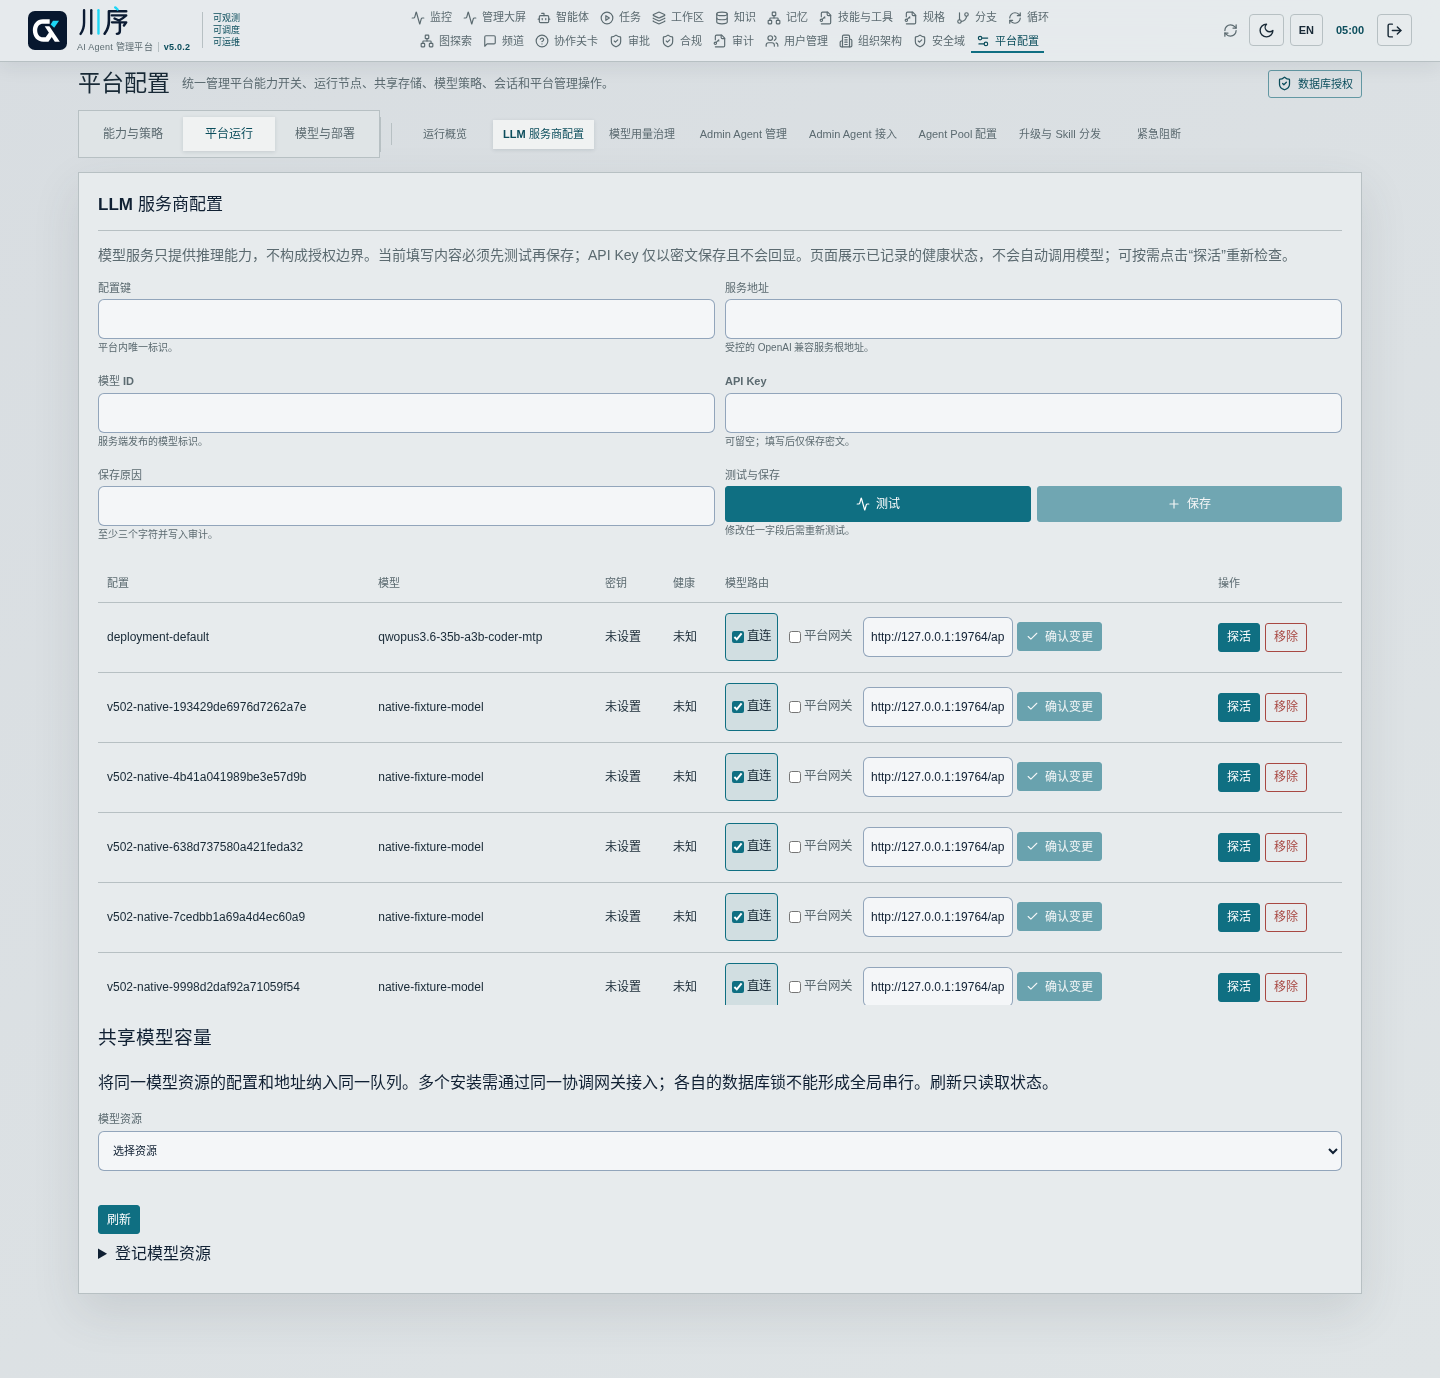
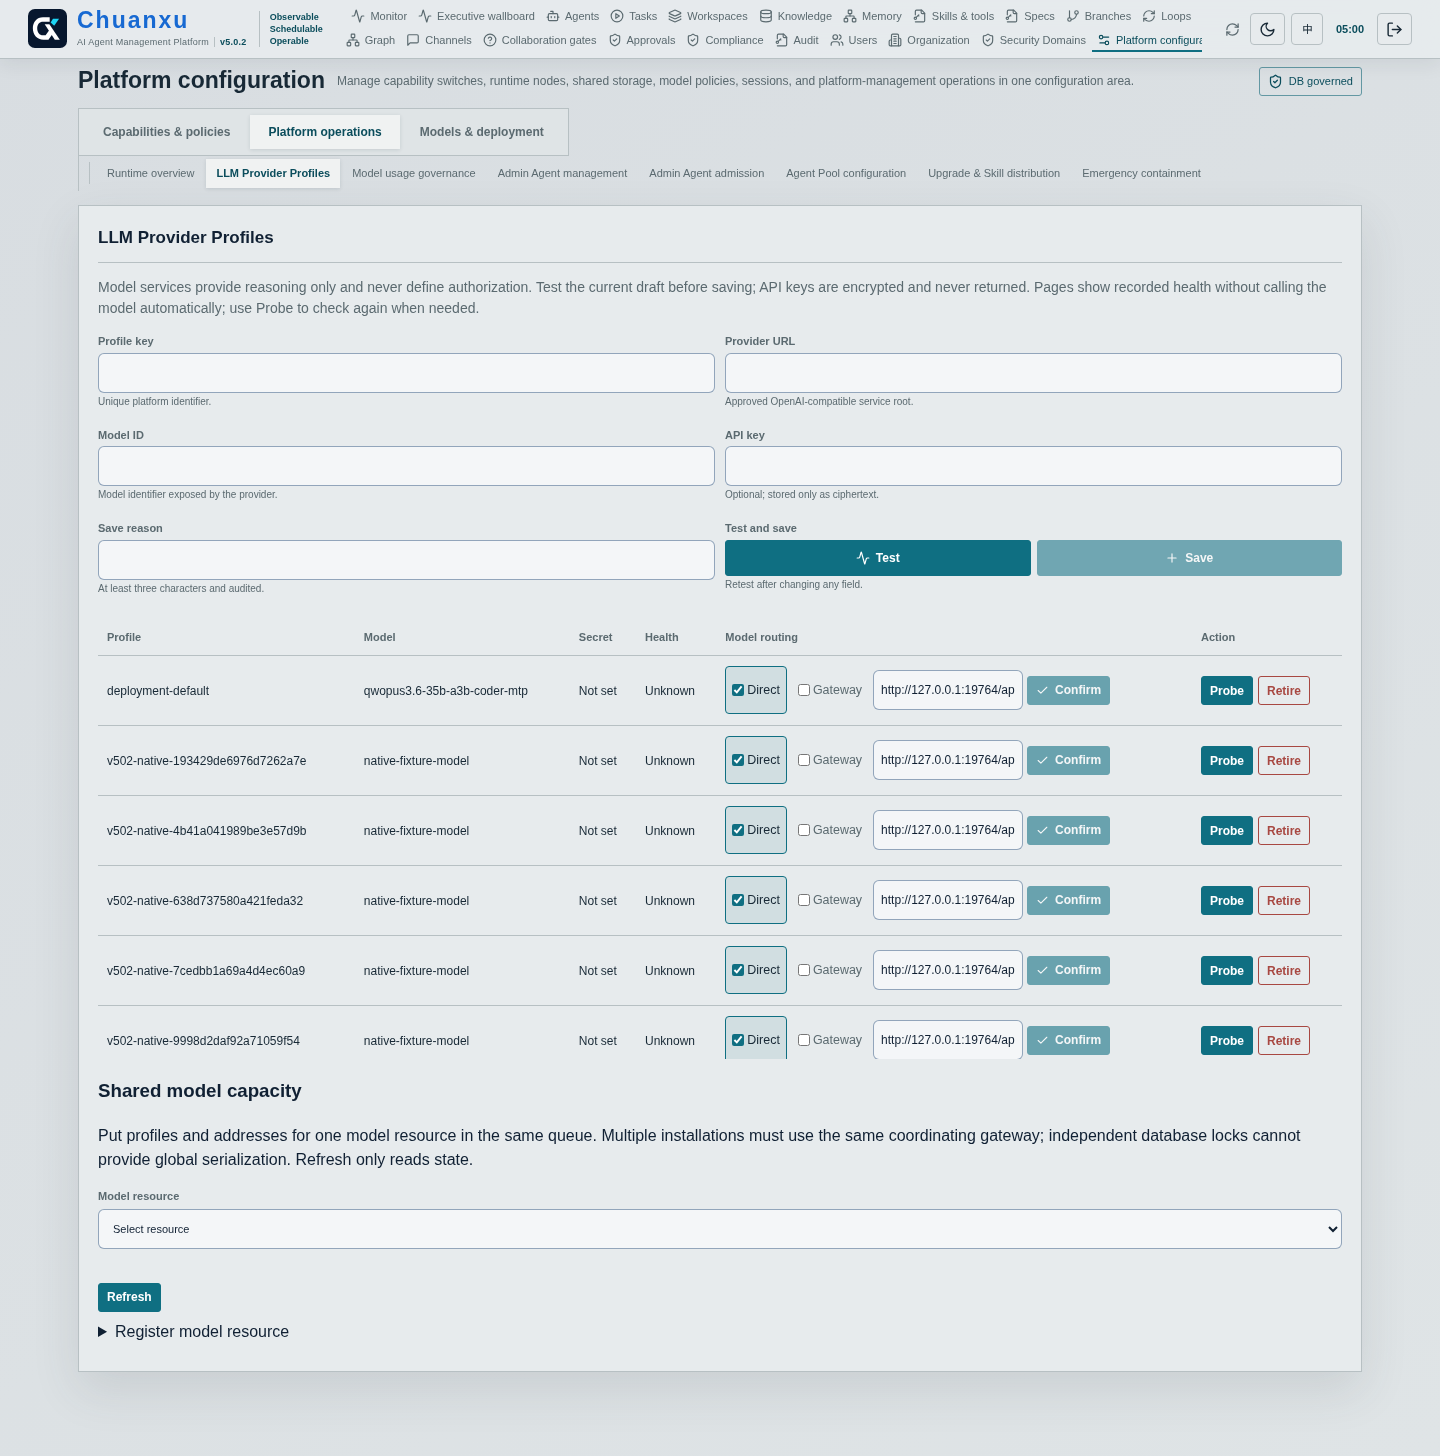
每个 LLM 服务商配置可以独立启用直连、平台网关或两者并行。管理员在同一行选择路由方式,确认变更并填写合规理由;转发地址由运行平台自动生成,不接受任意中转地址。网关执行硬配额或告警配额、原子预留与结算,并用 AES-GCM 保护有界幂等重放数据。经过可信路径的请求记录模型、Token 维度、来源、成本、延迟与状态,但不长期保存提示词和模型回答。Each LLM Provider Profile can independently allow direct access, the platform gateway, or both. An administrator selects routes on the same row, confirms the change, and records a compliance reason. The running platform generates the forwarding address and rejects arbitrary relay configuration. The gateway enforces hard or warning quotas, atomic reservation and settlement, and AES-GCM-protected bounded idempotent replay. Requests through trusted paths retain model, Token dimensions, provenance, cost, latency, and status without retaining prompts or model responses as long-term telemetry.
服务商账单导入进入追加式对账,企业平衡分摊把可核验费用分配到使用者、Agent 和组织;外部证据必须签名。绕过网关且没有可信适配器证据的调用明确标记为 UNOBSERVED,不制造“全量可见”的假象。Provider invoice imports enter append-only reconciliation, while enterprise-balanced allocation assigns verified cost to users, Agents, and organizations. External evidence must be signed. Calls outside the gateway remain UNOBSERVED without trusted adapter evidence; the product never implies complete visibility.
企业管理者视图Executive Operating Picture
一个登录后只读大屏,同时看平台运行与模型消耗One Authenticated Read-only View for Platform Operations and Model Consumption
管理大屏汇总 Agent 总量、在线、忙碌与停滞状态,活动会话、运行任务计划与循环,并以近 14 日曲线展示 Token 和成本变化。页面同时给出受限模型用量、网关覆盖率、生成时间与新鲜度。大屏没有确认、审批、导出、配置、模型探活或 Agent 调用入口,适合企业管理者持续查看而不扩大操作权限。The wallboard combines total, online, busy, and stalled Agents with active Sessions, running Task Plans and Loops, then plots 14-day Token and cost curves. It also presents bounded model usage, gateway coverage, generation time, and freshness. There are no acknowledge, approve, export, configure, provider-test, or Agent-invocation actions, making it suitable for continuous executive viewing without expanding operational authority.
v5.0.1 Product Baseline
身份、组织、协作与受治理记忆进入同一管理界面Identity, Organization, Collaboration, and Governed Memory Share One Management Surface
版本化记忆将当前可用版本、候选复核、逻辑不可用和持久作业纳入可审计生命周期;关系图只显示当前可用版本与必要历史谱系端点,历史节点不会自动进入运行上下文。实体关系视图只保留节点与拓扑连线,不叠加难以阅读的关系文字。Versioned memory places current usable versions, candidate review, logical unavailability, and durable jobs in an auditable lifecycle. Its graph shows only usable versions and necessary lineage endpoints; historical nodes never enter runtime context automatically. The entity relationship view keeps node identity and topology without unreadable edge text.
用户管理提供只读的有效访问模拟:管理员选择一个动作,查看该用户在角色、组织、安全域、委派和显式拒绝共同作用下的最终授权结果;模拟不会修改权限。User Management provides a read-only effective-access simulator: an administrator selects one action and sees the final decision produced by roles, organization, security domain, delegation, and explicit deny. Simulation never changes permissions.
资产与身份Estate and Identity
先知道企业中有哪些人和 AgentKnow the Human and Agent Estate First
v5.0.1 将每个普通平台账号、Human Principal 与组织人员统一为同一主体;注册审批必须选择主组织并原子写入账号与归属。一次性 Agent Enrollment Token 同时确定发起人和 Agent 归属。受保护的 bootstrap admin 是唯一不代表自然人的系统账号,固定保留最高管理能力。v5.0.1 unifies every ordinary platform account, Human Principal, and organization person as one subject. Registration approval must select a primary organization and atomically create both account and membership. A one-time Agent Enrollment Token also binds sponsor and Agent ownership. The protected bootstrap admin is the sole system account that does not represent a natural person and permanently retains top-level administration.
人员主体Human Principal
新批准用户默认仅进入 Portal;管理员填写原因后才能开启 App,入口变更会撤销其活动会话。Newly approved users default to Portal-only; enabling App requires an administrator reason and revokes active Sessions.
Agent 主体Agent Principal
Token 默认将签发人绑定为 Sponsor 和唯一 Human Primary Owner;替他人注册需要额外授权。By default, the Token binds its issuer as Sponsor and the sole Human Primary Owner; enrolling for another owner requires extra authority.
权限驱动界面Permission-driven UI
管理员拥有全局视图;其他用户仅看到授权范围。菜单和受保护视图标签用于表达边界,真正授权始终由服务端执行。Administrators have a global view; other users see only their assigned scope. Navigation and Protected View labels communicate boundaries, while authorization is always enforced server-side.
v5.0.1 平台管理与连续性v5.0.1 Administration and Continuity
把管理协作、升级和隔离放进受保护控制面Place Administration, Upgrade, and Containment in a Protected Control Plane
平台初始化创建一个受保护的平台管理频道。首次部署或新增节点时,优先由已有可信 Admin Agent 自动完成节点接入、身份材料生成和登记,不再要求管理员手工填写身份公钥;只有外部 Admin Agent 才走独立的身份验证与审批路径。它不是普通协作频道:只有受保护管理员、已启用的平台管理 Agent 和经身份验证、观察及独立审批后加入组的 Admin Agent 可使用;业务 Agent 不能读取、加入或通过普通注册获得该权限。生产建议配置 3 个健康 Admin Agent,使用 5、4、3 等互异正整数权重,同时要求人数多数和权重多数。数据库记录 Leader 任期、租约与围栏令牌,恢复的旧 Leader 无法提交陈旧控制写入。Platform initialization creates one protected Platform Administration Channel. For first deployment or a new node, an existing trusted Admin Agent can perform admission, identity-material generation, and registration automatically, so administrators do not need to enter an identity public key manually. External Admin Agents continue through a separate identity-proof and approval path. It is not a normal collaboration Channel: only the protected administrator, enabled platform management Agents, and Admin Agents admitted through identity proof, observation, and separate approval may use it. Business Agents cannot read, join, or obtain it through ordinary enrollment. Production recommends three healthy Admin Agents with distinct positive weights such as 5, 4, and 3, requiring both member-count and weighted majorities. The database records Leader terms, leases, and fencing tokens so a recovered former Leader cannot submit stale control writes.
安全域先于协作Security Domain Before Collaboration
安全域记录用途、密级、责任人、明确成员、有效期与原因,是频道和运行时重新校验的唯一授权边界。A Security Domain records purpose, classification, owner, explicit members, validity, and reason. It is the sole authorization boundary rechecked by Channels and runtime operations.
内部兼容执行Internal Compatibility Execution
历史协作组不进入客户配置面,仅为旧执行记录保留内部兼容关系;授权始终来自安全域。Legacy collaboration groups stay outside customer configuration and retain internal compatibility relations for historical execution records only; authority always comes from Security Domains.
分级隔离Staged Containment
先排空或隔离并撤销平台权限,再请求内存清理和停止。未配置适配器时,不宣称已经远程终止进程。Drain or quarantine first and revoke platform authority before requesting memory cleanup and stop. Without an adapter, no remote process termination is claimed.
Dashboard 和 Portal 的空闲与绝对会话时长独立由数据库策略控制。大型清单采用与当前主体、过滤、排序和页大小绑定的服务端游标分页,避免浏览器一次读取完整库存。Dashboard and Portal idle and absolute session durations are independently controlled by database policy. Large inventories use server-side cursors bound to the current Principal, filters, sort order, and page size instead of loading a full inventory in the browser.
v5.0.1 安全域治理v5.0.1 Security Domain Governance
先确定安全域,再组织频道和协作Establish the Security Domain Before Channels and Collaboration
安全域是频道协作的唯一授权与数据边界,记录用途、密级、责任人、显式人员与 Agent 成员、有效期和原因。频道、消息、提示词、Skill、Tool、API、工作区和图关系都不能单独扩大权限;每次频道列举、读取、发送、成员变更和 Gateway 交付都会重新检查当前安全域成员资格。受保护平台管理频道中的显式 @ 管理 Agent 请求会受控派发,并以可审计的 Markdown 回复回写频道。A Security Domain is the sole authorization and data boundary for Channel collaboration. It records purpose, classification, owner, explicit Human and Agent members, validity, and reason. Channels, messages, prompts, Skills, Tools, APIs, workspaces, and graph relationships cannot expand authority; Channel listing, read, send, membership changes, and Gateway delivery all re-check current domain membership. Explicit mentions of a management Agent in the protected administration Channel are dispatched through the control plane and write an auditable Markdown response back to the Channel.
显式成员与失效关闭Explicit Members and Fail-closed Expiry
成员撤销、暂停或过期后,后续读取、发送和运行时交付失败关闭,历史证据仍被保留。After member revocation, suspension, or expiry, later reads, sends, and runtime delivery fail closed while historical evidence remains preserved.
内部兼容关系不赋权Compatibility Relations Grant No Authority
历史协作组仅保留为内部兼容执行关系,不再作为客户可配置的授权或知识共享对象。Legacy collaboration groups remain internal compatibility execution relations only and are no longer customer-configurable authorization or Knowledge-sharing objects.
v5.0.1 数据库原生 SDDv5.0.1 Database-native SDD
让软件交付从文档协作进入数据库治理Move Software Delivery From Document Coordination Into Database Governance
数据库保存 Change、工作修订、批准基线、任务、评审、风险门禁、证据、SCM 连接和制品摘要。OpenSpec 可以生成或导入前期结构,但不控制执行阶段;多个 Agent 通过数据库中的 expected-version、读写集、租约和检查点协作,冲突或高风险状态自动暂停并等待处理。The database stores Changes, working revisions, approved baselines, tasks, reviews, risk gates, evidence, SCM connections, and artifact digests. OpenSpec can generate or import the early structure but does not control execution; multiple Agents coordinate through expected versions, read/write sets, leases, and checkpoints, while conflicts and high-risk states pause execution for review.
基线不可变Immutable Baseline
批准后的基线只读,后续变更必须产生新的工作修订并保留原因。Approved baselines are read-only; later changes create a new working revision with a reason.
协作可控Controlled Collaboration
任务角色、依赖、风险、资源租约和职责分离由数据库规则共同约束。Roles, dependencies, risk, resource leases, and separation of duties are jointly constrained by database rules.
证据可复核Reviewable Evidence
测试、评审、制品和 SCM 引用以摘要与来源留痕,形成可复核交付链。Tests, reviews, artifacts, and SCM references retain digests and provenance for a reviewable delivery chain.
v5.0.1 确定性部署v5.0.1 Deterministic Deployment
不依赖外部 Agent,也不让模型成为部署权限Deploy Without an External Agent or Model Authority
对已准备好的数据库目标,包内 Bootstrap Deployment Agent 先校验清单和前置条件,再执行被校验的包内 SQL,记录脱敏步骤、证据与本地节点租约,最后交接给平台管理 Agent 并退役。它不会自动创建 Oracle 或 YashanDB 的 PDB、表空间等高权限基础设施。For a prepared database target, the package-local Bootstrap Deployment Agent validates the manifest and prerequisites, then executes checked package SQL, records sanitized steps, evidence, and local-node leases, hands off to platform management Agents, and retires. It never creates Oracle or YashanDB PDBs, tablespaces, or other privileged infrastructure automatically.
部署证据Deployment Evidence
支持初始化、升级、续跑、状态与校验;未知部分模式或不匹配目标会失败关闭。Supports initialize, upgrade, resume, status, and verify; unknown partial schemas or mismatched targets fail closed.
嵌入契约Embedding Contracts
Profile、不可变 Contract、Space 与 Binding 约束模型、维度、度量、归一化、预处理和来源。Profiles, immutable Contracts, Spaces, and Bindings constrain model, dimension, metric, normalization, preprocessing, and provenance.
异步批量任务Asynchronous Batches
Dashboard 仅创建受审计任务;租约 Worker 在 HTTP 请求之外执行受限批量嵌入与重嵌入。The Dashboard creates audited jobs only; a leased Worker performs bounded embedding and re-embedding outside HTTP requests.
支持平台托管、企业直连、企业代理、预计算导入和禁用五种嵌入模式。不同 Contract、维度或预处理不能混入同一相似度或多模数据混合检索计算;历史向量保留在只读 `LEGACY_DEFAULT` 空间,需经授权重嵌入后再切换。Five Embedding modes are supported: platform managed, enterprise direct, enterprise proxy, precomputed import, and none. Different Contracts, dimensions, or preprocessing cannot enter one similarity or Multimodal Data Hybrid Retrieval calculation; legacy vectors remain in read-only `LEGACY_DEFAULT` until authorized re-embedding cutover.
v5.0.1 原生初始化v5.0.1 Native Initialization
没有现成 Agent,也可以从平台安全初始化Initialize Safely Even Without an Existing Agent
平台初始化可以直接创建 Platform Admin Agent;Enterprise 同时初始化受限的 Compliance Admin Agent。它们是独立的系统 Principal,不等同于人类 admin 用户,也不持有 Schema Owner 回退权限。没有批准的 LLM Profile 时,身份和锁定基线策略仍先进入数据库并保持待激活状态,模型可用性只决定激活,不阻断权威初始化。Platform initialization can create the Platform Admin Agent directly; Enterprise also initializes a restricted Compliance Admin Agent. They are independent system Principals, separate from the human admin user, and never use Schema Owner fallback. Without an approved LLM Profile, identities and locked baseline policies are still stored in the database as activation-pending; model availability gates activation but does not block authoritative bootstrap.
审批后创建受限 Agent Principal 和部署记录,Business Agent 始终禁止回退使用 Admin 或 Schema Owner 凭证。Approval creates a restricted Agent Principal and deployment record; Business Agents always fail closed and never fall back to Admin or Schema Owner credentials.
两条接入路径Two Access Paths
平台原生 Agent 与外部 Skill-first Agent 并存;外部注册开关可设为关闭、仅审批或开启。Platform-native and external Skill-first Agents coexist; external enrollment can be disabled, approval-only, or enabled.
客户已有虚拟化、SaaS、MaaS 或 Agent 平台通过 Deployment Adapter 契约对接;平台提供本地、远程 Worker、容器和 Webhook 的通用接入接口,客户专属连接器作为项目适配交付,并保留数据库授权、隔离、回调校验和审计边界。Customer virtualization, SaaS, MaaS, or Agent platforms connect through Deployment Adapter contracts. The platform provides generic local, remote-worker, container, and webhook integration interfaces; customer-specific connectors are delivered as project adapters while preserving database authorization, isolation, callback validation, and audit boundaries.
按需启用Scoped Enablement
按客户实际范围配置平台能力,不削弱安全控制面Configure the Product Surface Without Weakening the Security Plane
v5.0.1 将功能状态存入数据库,适用于 POC、分阶段上线和只启用必要模块的客户环境。有效能力同时受版本包、数据库实例开关与当前主体权限约束;开关不是授权机制,也不能扩大任何用户或 Agent 的权限。身份、授权、安全、审计写入、Agent、用户和平台配置等基础控制面强制保持启用。v5.0.1 stores capability state in the database for POCs, phased rollout, and installations that need only selected modules. Effective capability is constrained by edition contents, the database instance switch, and current Principal authorization. A switch never grants authority or expands any user or Agent permission. Identity, authorization, security, audit writes, Agents, users, and platform configuration remain mandatory.
三重有效边界Three-way Boundary
版本能力、实例开关和主体权限取交集,服务端与导航使用同一结果。Edition capability, instance switch, and Principal authorization intersect; server APIs and navigation use the same result.
保留数据Data Preserved
关闭功能不删除既有数据,仅阻止新入口和专属后台活动,便于恢复启用。Disabling preserves existing data while blocking new entry points and exclusive background activity.
不可关闭底座Mandatory Foundation
安全、身份、授权和审计写入等底座不可通过配置绕过。Security, identity, authorization, and audit-write foundations cannot be bypassed by configuration.
v5.0.1 企业版以数据库权威状态区分注册、运行、合规和控制状态。新 Agent 必须通过自身注册凭据完成 Gateway 激活证明;配置档案为不可变版本,例外要求补偿控制、有效期和不同的在职人员审批。确定性 Controller 仅依据受验证证据和规则投影姿态,不会把空闲、未调用 Skill 或模型不可用直接认定为违规。v5.0.1 Enterprise distinguishes registration, runtime, compliance, and control state through database-authoritative records. A new Agent must complete Gateway activation with its own registered credential; Profiles are immutable versions, and exceptions require compensating controls, expiry, and a distinct active Human approval. The deterministic Controller projects posture only from validated evidence and rules, never treating idleness, absent Skill use, or an unavailable model as a violation.
受限与隔离Restriction and Quarantine
受限状态仅保留心跳、证据、整改和恢复路径;隔离或禁用会撤销令牌并围栏活动实例。Restricted state retains only heartbeat, evidence, remediation, and recovery paths; quarantine or disable revokes tokens and fences active instances.
可复核处置Reviewable Response
发现、整改、例外与决策原因保留证据引用和审计链。Findings, remediation, exceptions, and decision reasons retain evidence references and an audit trail.
明确自动化边界Explicit Automation Boundary
当前系统身份不持有凭据、不批准例外、不执行控制变更;模型化合规建议仍是后续能力。The current system identity has no credential, exception-approval, or control-mutation authority; model-assisted compliance advice remains future work.
图形化组织治理Graphical Organization Governance
沿组织、人员与 Agent 责任关系快速查看和配置Inspect and Configure Organization, People, and Agent Accountability
v5.0.1 使用规整、确定性的分层画布呈现主组织、兼职组织、直属与虚线汇报、项目负责人,以及 Agent 主负责人、操作人与查看人。支持组织、人员归属、Agent 归属和异常关系四种视图;拖拽只生成语义变更草稿,不保存画布坐标,也不会绕过校验、影响分析和审批。v5.0.1 uses a regular deterministic hierarchy to show primary and secondary memberships, direct and dotted-line reporting, project leads, and Agent owners, operators, and viewers. Organization, people, Agent responsibility, and anomaly modes share one canvas. Dragging creates semantic draft operations only; it never stores coordinates or bypasses validation, impact analysis, or approval.
快速检索责任链Find Accountability Quickly
按授权范围搜索组织、人员和 Agent,聚焦子树并渐进展开;左侧范围、中央画布和右侧变更区均明确标记为受保护视图。Search authorized organizations, people, and Agents, focus a subtree, and expand progressively. The scope tree, central canvas, and change inspector are each explicitly marked as Protected Views.
图形不是授权源The Graph Does Not Grant Access
受保护视图不会先加载全企业数据,也不自行授予权限;主组织闭包、安全域、角色、显式拒绝与有效期始终在服务端共同决策。Protected Views neither load the enterprise for client filtering nor grant authority. Primary-membership closure, security domains, roles, explicit deny, and validity remain server-side decision inputs.
组织关联知识治理Organization-aware Knowledge Governance
公司共享、组织边界与个人私有知识使用同一策略模型Company-wide, Organizational, and Private Knowledge Share One Policy Model
知识条目可配置为全公司公开、组织子树、组织层级、人员私有或 Agent 私有。组织策略关联主组织结构和层级边界,使研发、财务、行政等范围按企业结构隔离;列表、详情、关系图与检索都执行同一服务端策略,不依赖浏览器过滤。A Knowledge item can be company-public, organization-subtree, organization-level, Human-private, or Agent-private. Organization policies bind to the primary organization hierarchy and level boundary, separating areas such as engineering, finance, and administration. List, item, graph, and retrieval paths enforce the same server-side policy rather than browser filtering.
Portal 与频道共用知识检索和模型披露策略。频道还按当前会话读者的授权交集筛选知识,在模型调用、回复发布和历史读取时重新检查来源与权限;未获授权的模型不会接收知识正文。Portal and Channels share knowledge retrieval and model-disclosure policy. Channels also filter Knowledge by current conversation-reader permissions and recheck sources and access before model dispatch, publication and historical reads. Models without disclosure authorization receive no Knowledge text.
持久工作模型Durable Work Model
从一次对话到长期、多 Agent 工作From One Conversation to Long-running Multi-Agent Work
记忆、知识、工作区、会话链、任务计划、分支、Loop 与 Graph Run 持久化在数据库中。安全域定义协作授权边界,频道承载互动与证据;历史协作组只保留为内部兼容执行关系。副作用操作具备策略、审批、租约、重试和幂等边界,进程异常后可以由替代实例恢复受管上下文。Memory, Knowledge, workspaces, session chains, task plans, branches, Loops, and Graph Runs persist in the database. Security Domains define collaboration authorization boundaries, Channels carry interaction and evidence, and legacy collaboration groups remain internal compatibility execution relations only. Side effects use policy, approval, leases, retries, and idempotency boundaries so replacement instances can rebuild managed context after failure.
协作关卡Collaboration Gate
多个 Agent 在关键节点汇合,先到者等待;可总结、讨论、Review、调整后继续。兼容标识仍为 Barrier,但产品术语统一为协作关卡。Agents converge at critical points; early arrivals wait for summaries, discussion, review, and adjustment before continuing. Barrier remains a compatibility identifier.
可变 Loop 与 GraphMutable Loop and Graph
执行过程可根据结果细化,但版本、变更原因、运行状态和证据始终持久化并可复核。Execution can evolve based on results while versions, reasons, runtime state, and evidence remain durable and reviewable.
受治理频道Governed Channels
像群聊一样查看协作,但频道成员关系不扩大权限Conversation-like Collaboration Without Permission Expansion
频道将人员、Agent、线程、消息、Action Card、制品和协作关卡汇集在可查看的工作流中。人和 Agent 都可以参与多个频道,但任何数据披露、Skill/Tool/API 调用和制品传输仍重新校验实际资源权限;跨安全域只能通过受治理 Bridge。Channels bring people, Agents, threads, messages, Action Cards, artifacts, and collaboration gates into a visible workflow. Humans and Agents may join multiple channels, but every disclosure, Skill/Tool/API call, and artifact transfer still re-checks resource authorization; cross-domain transfer requires a governed Bridge.
频道不是授权容器A Channel Is Not an Authorization Container
加入频道不自动获得数据库、知识、记忆、API、Skill、Tool、模型或导出权限,避免受损 Agent 借频道成员关系扩大影响面。Joining a channel never grants database, knowledge, memory, API, Skill, Tool, model, or export rights, limiting the blast radius of a compromised Agent.
受治理节点维护Governed Node Maintenance
先排空,再退役;运行中的任务不被强制中断Drain Before Retirement Without Forcing Running Work to Stop
管理员可以在受保护的平台管理频道中提出 Agent Pool 节点排空计划。请求先形成 Action Card,经过既有审批边界后,源节点停止接收新任务;仅过期且可重试的任务可以转移到活动目标节点,已经运行的任务继续完成。自然语言、提示词或模型回复本身不能授权执行。An administrator can propose an Agent Pool drain from the protected Platform Administration Channel. The request becomes an Action Card and follows the existing approval boundary before the source stops accepting new work. Only expired retryable work may move to an active destination; running work is allowed to finish. Natural language, prompts, and model output never authorize execution.
逻辑退役Logical Retirement
节点与 LLM 配置从活动清单和选择器中隐藏,但保留审计和历史记录。LLM 退役同时撤销已保存的加密 API Key 密文。Nodes and LLM profiles leave active inventory and selectors while audit and history remain. LLM retirement also revokes stored encrypted API-key ciphertext.
依赖先清理Clear Dependencies First
活动执行、Worker、接入流程、共享目录绑定、Admin HA 成员或模型策略仍在引用时,退役操作失败关闭。当前版本暂无可用 Agent Pool 节点,真实转移需在客户环境用实际节点验证。Retirement fails closed while active executions, workers, onboarding, storage bindings, Admin HA membership, or model policy references remain. The current release has no live Pool node, so transfer behavior requires validation on customer nodes.
Agent 网关Agent Gateway
隔离运行实例,缩小凭证和故障影响面Isolate Runtime Instances and Reduce Credential Blast Radius
同一逻辑 Agent 可以按安全域、频道、Task 或 Run 创建隔离实例,使用独立临时目录和短期凭证。实例受损时可以单独撤销、栅栏和隔离,而不必禁用其他正常实例。One logical Agent can create isolated instances by security domain, channel, task, or run, each with separate temporary files and short-lived credentials. A compromised instance can be revoked, fenced, and isolated without disabling healthy instances.
Memory Ecosystem
记忆生态与接口验证Memory ecosystem and interface verification
通用接口兼容、已实现专用适配器与确切版本组合实测是不同结论。PowerContext、TencentDB Agent Memory 的接入及同时运行须按实际版本、接口、认证与部署组合验证;生态名称、Logo、链接或发现结果不能证明专用适配或联合验收。Generic interface compatibility, implemented dedicated adapters and verified exact-version combinations are distinct conclusions. PowerContext and TencentDB Agent Memory integrations, including running both together, require evidence for the actual versions, interfaces, authentication and deployment combination. Ecosystem names, logos, links and discovery do not prove a dedicated adapter or joint acceptance.
统一界面Unified Interface
22 个 Dashboard 主要管理视图Primary Dashboard Views
监控、智能体、组织架构、任务、工作区、知识、记忆、技能、规格、分支、循环、图探索、频道、安全域、协作关卡、审批、审计、用户管理、合规、平台配置和功能配置等主要视图使用统一品牌视觉与权限模型。Graph Runtime 核心与授权检查属于稳定生产基线。草稿导入、SLO 只读检查与检查点分叉独立受控;已登记 MCP、A2A、仅元数据遥测和固定隔离框架按各自授权启用。离线回放与迁移预检只分析持久事实,真实副作用回放、运行中迁移、任意框架执行与全局自治保持关闭。Monitor, Agents, Organization, Tasks, Workspaces, Knowledge, Memory, Skills, Specs, Branches, Loops, Graph, Channels, Security Domains, Collaboration Gates, Approval, Audit, User Management, Compliance, Platform Configuration, and Capability Configuration are primary views sharing one visual and authorization model. Graph Runtime core and authorized inspection remain available. Draft import, read-only SLO views and checkpoint forks are independently controlled. Registered MCP, bounded A2A, metadata-only telemetry and one pinned isolated framework use separate authorization. Offline replay and migration preflight inspect persisted facts; live effect replay, live migration, arbitrary frameworks and global autonomy remain disabled.
真实边界Honest Boundary
管理范围取决于受控接入Governance Depends on Controlled Adoption
平台不会无条件发现未安装 Skill、未注册或绕过平台的 Agent;无法撤回已经导出或缓存的数据,也不能自动终止平台控制面外的进程。外部 API 和 Tool 只有经平台执行面或受控凭证分发时才能统一阻断。The platform cannot unconditionally discover Agents that have not installed a Skill, registered, or used controlled routes. It cannot retract exported or cached data, nor terminate processes outside its control plane. External APIs and Tools can be blocked centrally only when routed through the execution plane or controlled credential delivery.